Not Sure if CMMC Applies to You?
If you handle defense-related drawings, specs, schedules, or contract data—then it likely does.
Take the QuizUnderstand CMMC Level 2 requirements and what compliance means for you
Safeguard sensitive data and control access across global ecosystems
Streamline regulatory adherence and audit readiness in complex environments
Enable secure partner engagement and transparent transactions
Optimize payment cycles and minimize disruptions from end-to-end
Run compliant, efficient sourcing events and contract execution
Centralize and automate supplier lifecycle and credentialing workflows
Accelerate clinical trial timelines by simplifying site activation and access
Meet DEA requirements with secure, identity-proofed e-prescription workflows
Achieve CMMC Level 2 compliance with a fully managed solution
A secure supplier management solution that simplifies onboarding, compliance, and data verification with access to large pre-verified Exostar Partner Network
A secure, centralized access point that verifies every user in the Exostar Network, enabling trusted, compliant collaboration across aerospace & defense organizations
A secure Microsoft Teams environment for CMMC compliance and secure collaboration
A secure web-based solution that streamlines supply chain management through supplier system integration, automation, and compliance
Simplifies application access, reduces tech burdens and accelerates clinical study start-up through seamless authentication and a trusted life sciences community
Streamlines CMMC/NIST SP 800-171 self-assessments, calculates SPRS scores, and generates SSPs and POA&Ms for compliance
Streamline order-to-cash by automating customer communication, aligning demand with production, and enabling real-time, proactive issue resolution
A versatile IAM solution for banking, financial services, and insurance, providing secure access, SSO, adaptive authentication, and identity governance for employees, partners, and customers
Policy management and optimization for NIST SP 800-171 & CMMC compliance
Streamlines RFxs and auctions for regulated industries, helping procurement teams source faster, stay compliant, and engage suppliers more effectively
A DEA-compliant electronic prescribing of controlled substances (EPCS) solution that enables secure access for ensuring identity proofing, 2FA authentication, digital signature and seamless EHR/EMR integration
Your central hub for logging in, accessing technical support, and finding helpful resources across Exostar’s solutions.
find user login and support hereSimplify policy management & CMMC compliance with Exostar PolicyPro™. Easily create, store, & optimize policies with our library, ensuring DoD cybersecurity standards alignment.
As of July 13, the Department of War (DoW) has suspended the requirements for CMMC Phase 2 implementation, and the program is under a 60-day review. We are actively updating our content to reflect the latest information. Guidance for protecting Controlled Unclassified Information (CUI) and supporting NIST SP 800-171 remains unchanged.
If you handle defense-related drawings, specs, schedules, or contract data—then it likely does.
Take the QuizPolicies are written to reflect how the organization actually operates.
Refine and regenerate policy language as environments evolve.

Keep documentation current without manual rewrites.

Six Questions Every Organization Must Ask Themselves to Achieve CMMC Level 2
This infographic outlines a clear, step-by-step path to CMMC Level 2, framed around the six critical questions every organization must address to reach certification and sustain compliance over time.
Navigating the complexities of CMMC 2.0 can feel like building a bridge mid-flight. One of the most common challenges organizations face is the lack of comprehensive policy documentation. This gap can lead to costly delays or even lost contracts during assessments.
CMMC 2.0 isn’t just guidance. Beginning November 10, 2025, it becomes a contractual requirement for organizations seeking DoD business. The framework standardizes cybersecurity practices and protects Controlled Unclassified Information (CUI) across the defense supply chain.
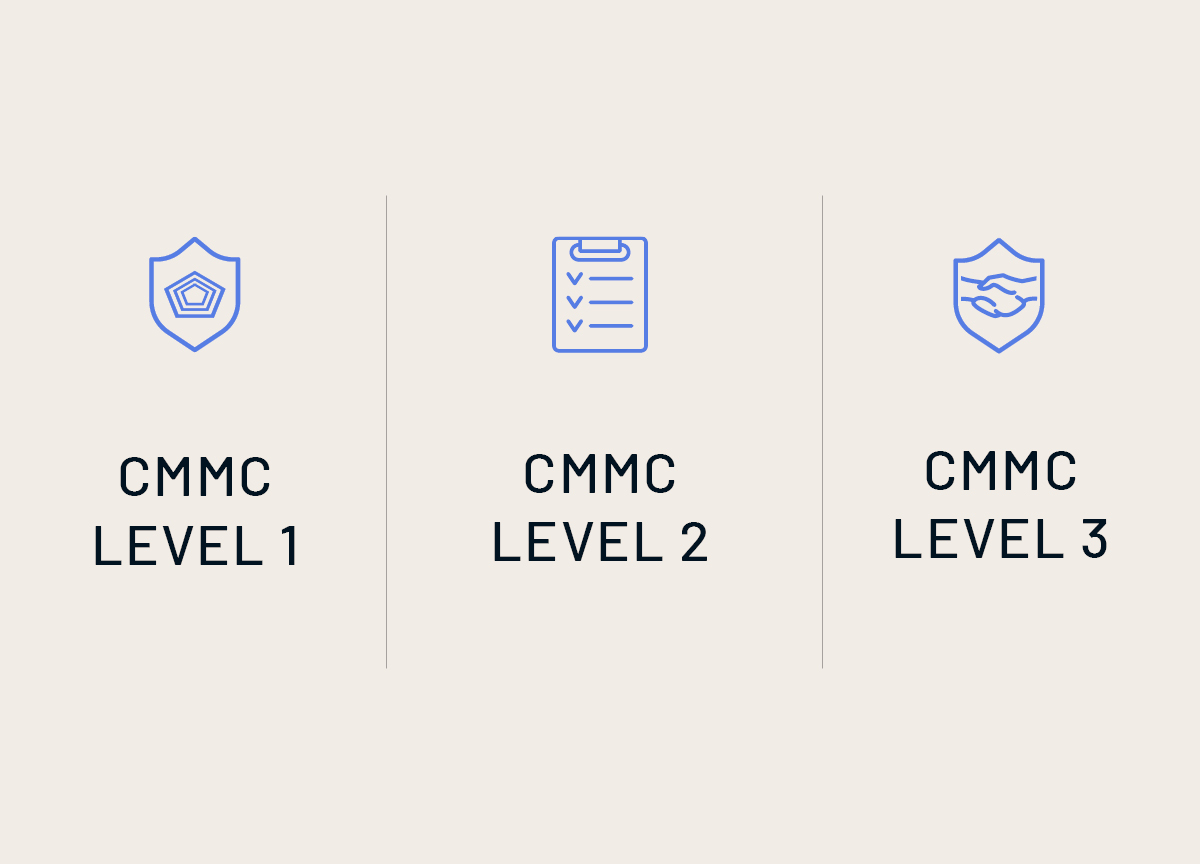
Achieving cybersecurity maturity under CMMC 2.0 requires more than just technical controls. It also demands strong documentation and clear evidence of compliance across the Defense Industrial Base (DIB). While the updated model reduces complexity through its three-level structure, it still imposes strict security requirements. At every level, effective policy management plays a vital role in achieving and maintaining compliance.
If you work on DoD contracts or support a prime contractor, CMMC compliance is not optional, it’s required. Act now.
Get started with smarter, faster policy creation and management. Whether you’re building from scratch or refining existing documentation, get the tools and guidance to align with NIST SP 800-171 and CMMC 2.0—no consultants required. Submit the form to connect with a policy expert and explore how PolicyPro can simplify your compliance journey.
Your request has been received, and a member of our team will be in touch shortly to discuss how you can simplify and accelerate your CMMC policy compliance. We look forward to helping you move forward with confidence.
Looking for help? Ask about additional tools and support services to accelerate your readiness.